Every request that your application sends to the Business Profile APIs must
include an authorization token. The authorization token identifies the user or
the application to Google, which allows access to the Business Profile APIs.
Your application must use [OAuth 2.0](https://developers.google.com/identity/protocols/OAuth2)
protocol to authorize requests.
This guide explains the different methods that you can use to implement
OAuth 2.0 on your platform. The [Google Identity Platform](https://developers.google.com/identity/choose-auth)
provides the Google Sign-In and OAuth functionality that's used throughout this
guide.
In order to further understand how to user Oauth 2.0 for web server
applications, please refer to the [guide here](https://developers.google.com/identity/protocols/oauth2/web-server).
The implementation of OAuth 2.0 provides the following benefits:
- Protects access to the business owner's data.
- Establishes the identity of the business owner when they sign in to their Google Account.
- Establishes that a partner platform or application can access and modify location data with explicit consent from the business owner. The owner can later revoke this access.
- Establishes the identity of the partner platform.
- Enables partner platforms to perform online or offline actions on behalf of the business owner. This includes responses to reviews, creation of posts, and updates to menu items.
## API Access with OAuth 2.0
Before you begin, you need to configure your Google Cloud project and enable the
Business Profile APIs. For more information, see the documentation for
[Basic setup](https://developers.google.com/my-business/content/basic-setup).
### Configure OAuth and the consent screen
Follow these steps to create credentials and the consent screen:
1. From the [Credentials page](https://console.developers.google.com/apis/credentials) in the API Console, click **Create credentials** and select "OAuth Client ID" from the drop-down list.
2. Select your application type, fill in the relevant information, and click **Create**.
3. Click **Save**.
4. Update the [OAuth consent screen settings](https://console.developers.google.com/apis/credentials/consent). From there, you can update the application name and the logo, as well as include a link to your terms of service and privacy policy.
The following image shows the application name and logo fields on the OAuth
consent screen:

The following image shows additional fields that appear on the OAuth consent
screen:

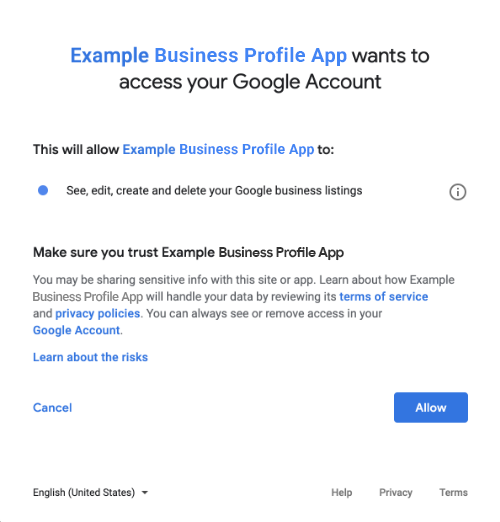
The following image is an example of what the user might see before they provide
consent:
### Methods to incorporate OAuth 2.0
You can use the following methods to implement OAuth 2.0:
- [Client libraries](https://developers.google.com/my-business/content/implement-oauth#client-libraries)
- [Google Sign-In](https://developers.google.com/my-business/content/implement-oauth#sign-in)
- [Offline access](https://developers.google.com/my-business/content/implement-oauth#offline-access)
- [Online access only](https://developers.google.com/my-business/content/implement-oauth#online-access)
The following content provides information about these methods to incorporate
OAuth 2.0 into your application.
#### Authorization Scopes
Requires one of the following OAuth scopes:
- https://www.googleapis.com/auth/business.manage
- https://www.googleapis.com/auth/plus.business.manage
The plus.business.manage scope has been deprecated and is available to maintain
backward compatibility for existing implementations.
#### Client libraries
The language-specific examples on this page use [Google API Client Libraries](https://developers.google.com/api-client-library/)
to implement OAuth 2.0 authorization. To run the code samples, you must first
install the client library for your language.
Client libraries are available for the following languages:
- [Go](https://github.com/google/google-api-go-client)
- [Java](https://developers.google.com/api-client-library/java/)
- [.NET](https://developers.google.com/api-client-library/dotnet/)
- [Node.js](https://github.com/google/google-api-nodejs-client/)
- [PHP](https://developers.google.com/api-client-library/php/)
- [Python](https://developers.google.com/api-client-library/python/)
- [Ruby](https://developers.google.com/api-client-library/ruby/)
#### Google Sign-In
[Google Sign-In](https://developers.google.com/identity/) is the quickest way to
integrate OAuth into your platform. It's available for Android, iOS, Web,
and more.
[](https://developers.google.com/identity/)
[](https://developers.google.com/identity/)
Google Sign-In is a secure authentication system that enables users to sign in
with their Google Account, which is the same account that they use to sign in to
other Google services. Once the user is signed in, they can grant consent for
your application to call the Business Profile APIs and exchange the
authorization code that's used to obtain refresh and access tokens.
#### Offline access
You might want to call the Business Profile APIs on behalf of a user even when
the user is offline. It's recommended that platforms incorporate this
functionality because you can edit, view, and manage listings anytime after the
user has signed in and granted consent.
Google assumes that the user is already signed in with their Google Account, has
granted consent for your application to call the Business Profile APIs, and
exchanged an authorization code that's then used to obtain a refresh token, and
later, an access token. The user can store the refresh token securely and use
it later to obtain a new access token at any time. For more information, read
[Google Sign-In for server-side
apps](https://developers.google.com/identity/sign-in/web/server-side-flow).
The following code snippet shows how to implement offline access in your
application. To run this code, see [Run the sample](https://developers.google.com/my-business/content/implement-oauth#run-sample).
> [!WARNING]
> **Warning:** This code is meant for demonstration purposes. Never expose your API key on the client side.
```
Business Profile Offline Access Demo
This demo demonstrates the use of Google Identity Services and OAuth to gain authorization to call the Business Profile APIs on behalf of the user, even when the user is offline.
When a refresh token is acquired, store this token securely on your database. You will then be able to use this token to refresh the OAuth credentials and make offline API calls on behalf of the user.
The user may revoke access at any time from the Account Settings page.
API Responses:
```
#### Online access only
For ease of implementation, calls from Business Profile APIs might be performed
without caching user refresh tokens. However, the user is required to be signed
in for the platform to perform API calls as the user.
The following code snippet demonstrates implementation of the Google Sign-in
flow and how to make a user-specific API call. After the user signs in with
their Google Account and grants consent to your application, an access token is
granted. This access token identifies the user and is required to be passed as a
header in the Business Profile APIs request.
To run this code, see [Run the sample](https://developers.google.com/my-business/content/implement-oauth#run-sample).
```
```
> [!NOTE]
> **Note:** For more information about integration, see [Sign In With Google](https://developers.google.com/identity/gsi/web).
### Run the sample
Perform the following steps to run the sample code provided:
1. Save the code snippet into a file titled `index.html`. Make sure you have your client ID set in the file.
2. Start the web server with the following command from your working directory:
### Python 2.X
```
python -m SimpleHTTPServer 8000
```
### Python 3.X
```
python -m http.server 8000
```
3. From the [Credentials](https://console.developers.google.com/apis/credentials)
page in the API Console, select the client ID used.
4. Under the *Authorized JavaScript origins* field, enter your website URL. To
run the sample code in this guide, you must also add `http://localhost:8000`.
5. Load the following URL into your browser:
```
http://localhost:8000/index.html
```